

Sandbox Execution
PraisonAI CLI provides sandboxed execution for running AI-generated commands safely. Inspired by Codex CLI’s sandbox modes, this feature isolates command execution with configurable security policies.The
praisonai code coding agent has its own OS-level containment for every shell command — Seatbelt (macOS) or bwrap (Linux), driven by PRAISON_SHELL=sandboxed. It is the path that actually runs on macOS today, distinct from SandboxConfig.native() (Linux-only sandlock). See OS Sandbox.Overview
The sandbox provides:- Command validation - Block dangerous commands
- Resource limits - CPU, memory, and time limits
- Path restrictions - Control filesystem access
- Network isolation - Optional network blocking
- Execution isolation - Separate working directory
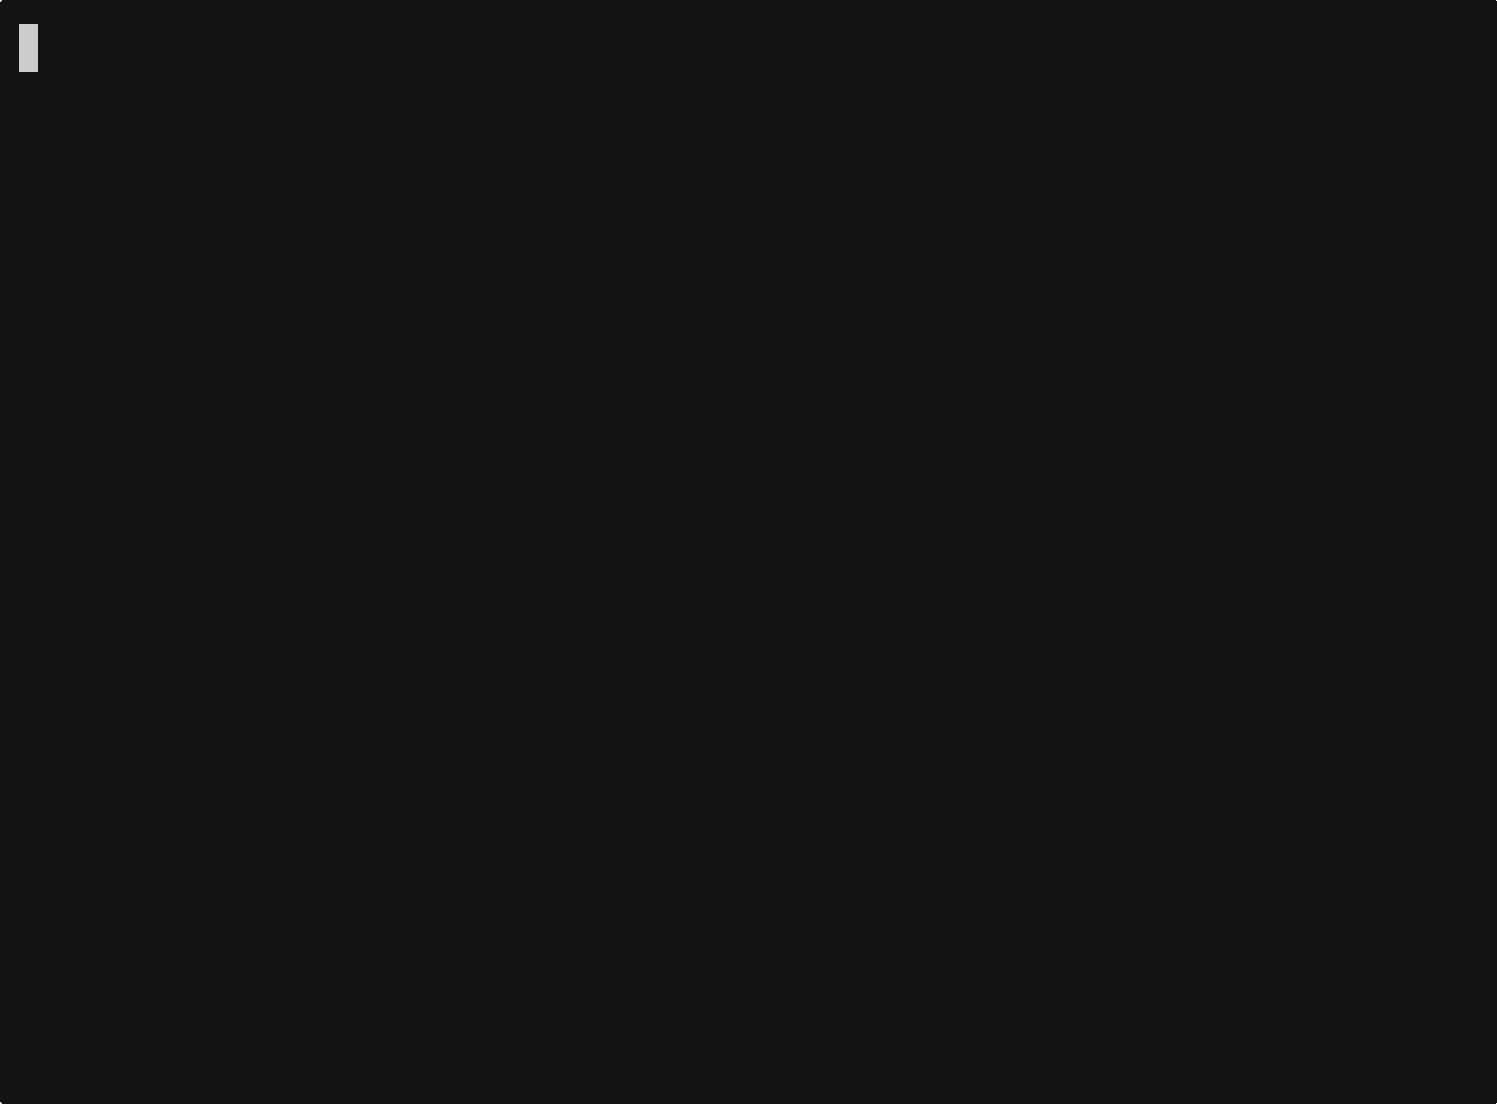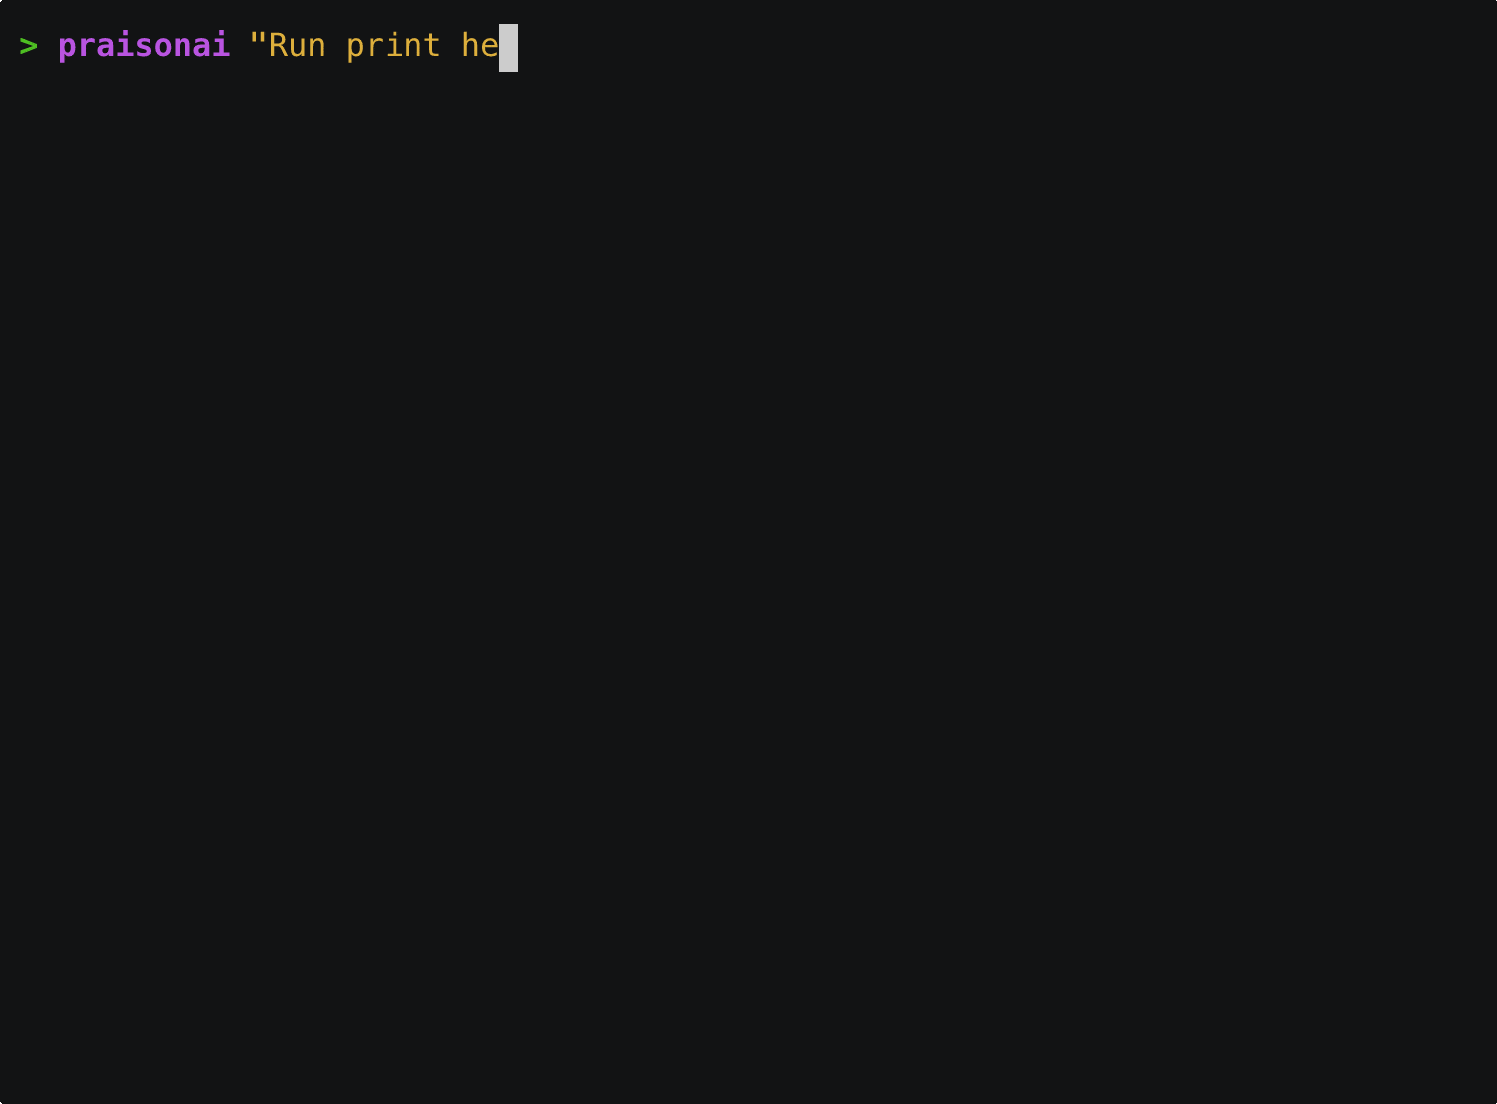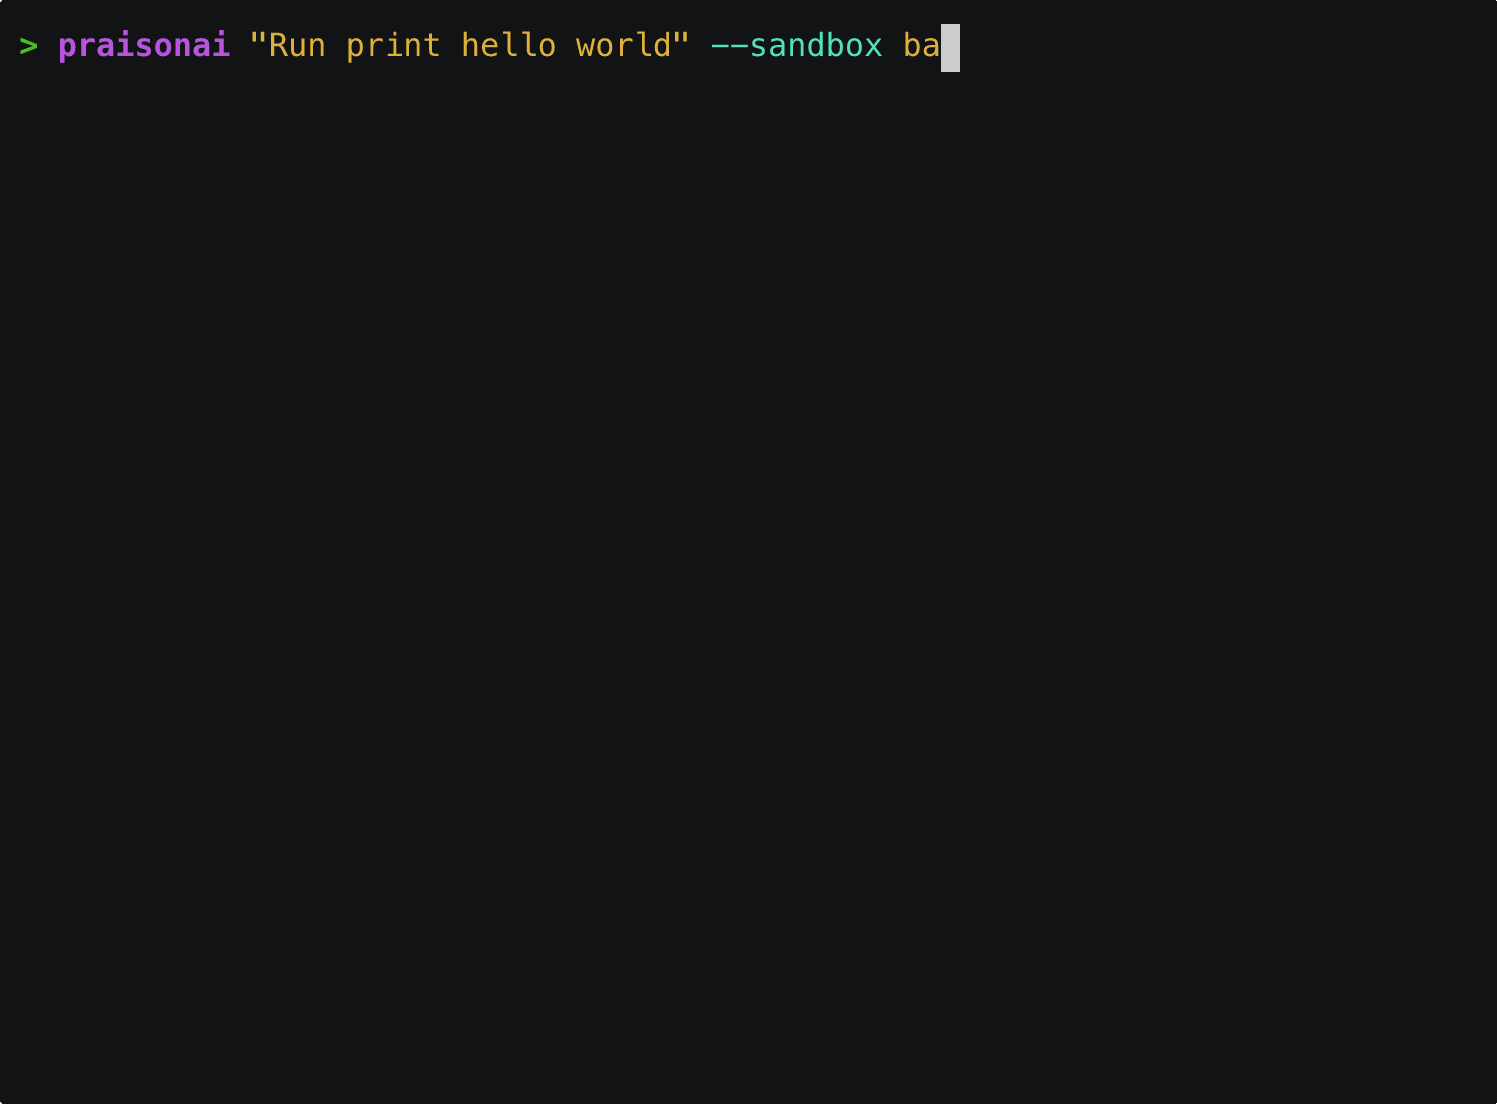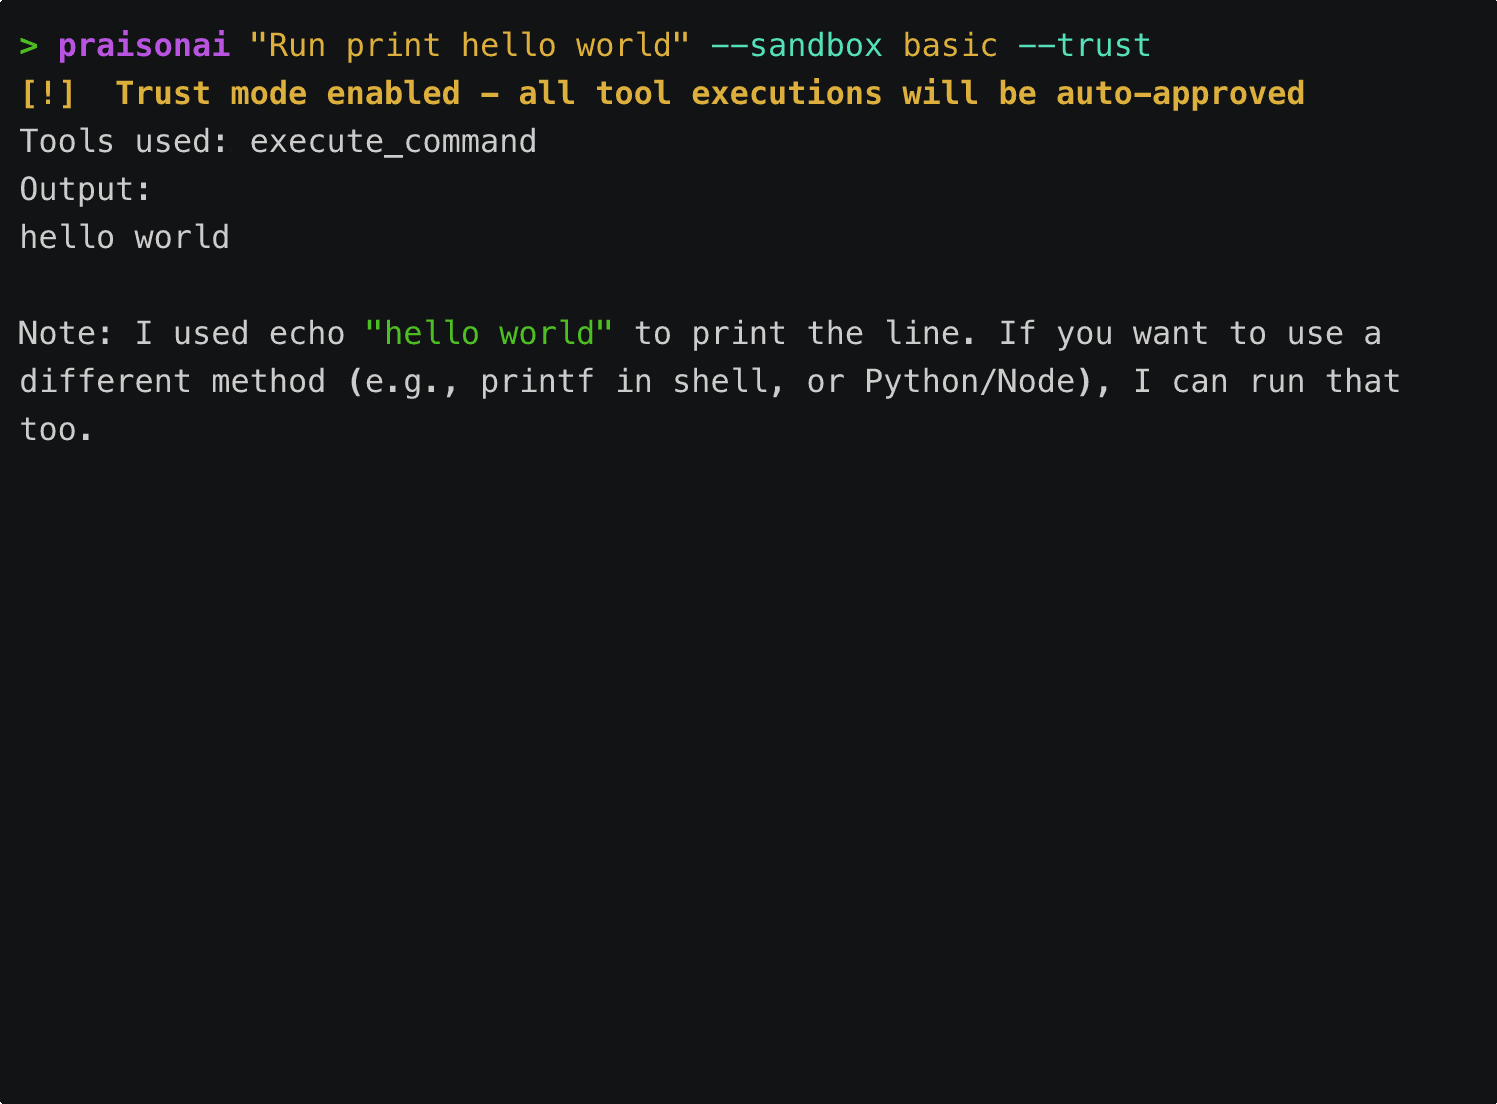
Quick Start
Sandbox Modes
Disabled (Default)
No sandboxing. Commands run normally.Basic
Light sandboxing with resource limits:- ✅ 512MB memory limit
- ✅ 60 second timeout
- ✅ Blocked dangerous commands (rm -rf, sudo, etc.)
- ✅ Network access allowed
Strict
Heavy sandboxing with filesystem isolation:- ✅ 256MB memory limit
- ✅ 30 second timeout
- ✅ Blocked dangerous commands
- ✅ Blocked network tools (curl, wget, etc.)
- ✅ Isolated temporary directory
- ✅ Limited process count (5)
Network Isolated
No network access:- ✅ 512MB memory limit
- ✅ 60 second timeout
- ✅ Blocked dangerous commands
- ❌ No network access
Python API
Basic Usage
Execution Result
Command Validation
Custom Policy
Blocked Commands
By default, these commands are blocked:Strict Mode Additional Blocks
Dangerous Patterns
These patterns are always blocked:Path Restrictions
Blocked Paths (Strict Mode)
Allowed Paths
Resource Limits
Memory Limit
CPU Time Limit
Process Limit
Integration with Autonomy Modes
Sandbox works with autonomy modes:Error Handling
Timeout
Policy Violation
Execution Error
Best Practices
When to Use Sandbox
Security Tips
- Start with strict - Relax restrictions as needed
- Review violations - Check what’s being blocked
- Use network isolation - When network isn’t needed
- Set timeouts - Prevent runaway processes
- Limit resources - Prevent resource exhaustion
Environment Variables
CLI Flags
The legacy--sandbox off|basic|strict flag only prints a not-enforced warning; it does not use this executor. For containment from the CLI:
Troubleshooting
Command Unexpectedly Blocked
Timeout Too Short
Path Access Denied
Related Features
- Autonomy Modes - Control AI autonomy
- Git Integration - Safe code changes
- Slash Commands - Interactive commands